Top Privacy Policy Mistakes After Acquisitions
When companies merge or acquire others, privacy policies often get overlooked, leading to serious legal and financial risks. Missteps like failing to update policies, ignoring consent requirements, or inheriting vulnerabilities can result in fines, lawsuits, and reputational harm. For example:
 Samson JagorasPrincipal & CEO/CIOJanuary 2, 2026
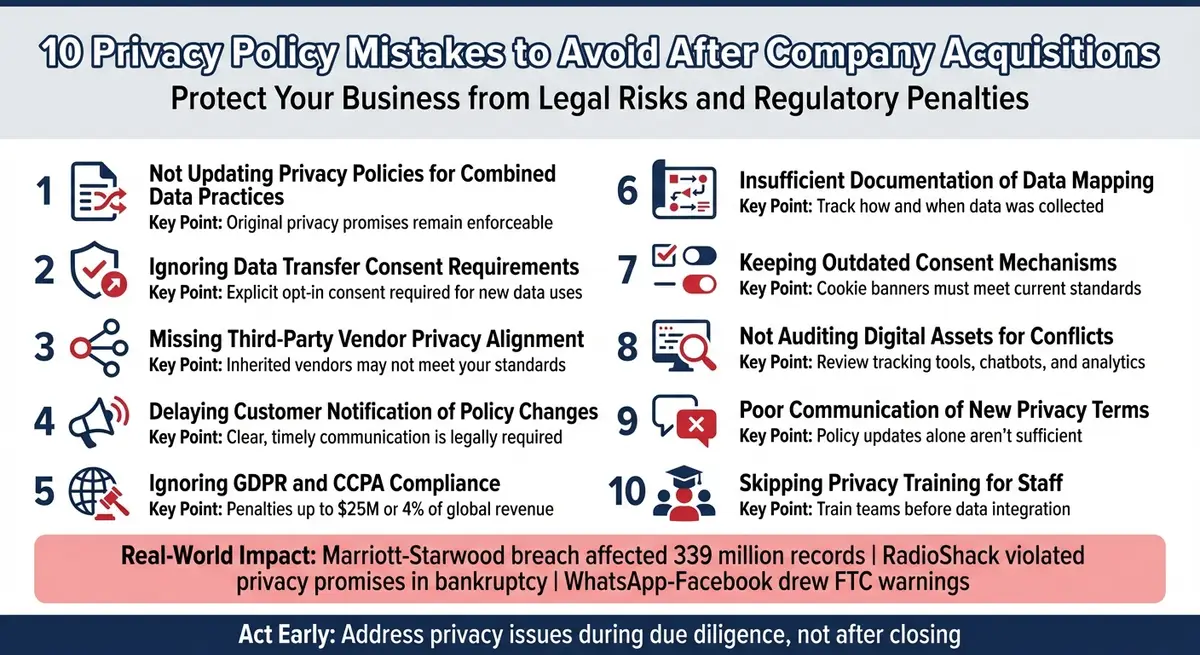
When companies merge or acquire others, privacy policies often get overlooked, leading to serious legal and financial risks. Missteps like failing to update policies, ignoring consent requirements, or inheriting vulnerabilities can result in fines, lawsuits, and reputational harm. For example:
- Marriott-Starwood Case: A breach affecting 339 million records remained undetected post-acquisition, leading to major liabilities.
- RadioShack Bankruptcy: Privacy promises were violated during a data sale, triggering intervention by 38 states.
- WhatsApp-Facebook: Privacy updates without proper consent drew FTC warnings and user backlash.
Key challenges include aligning privacy policies, ensuring compliance with laws like GDPR and CCPA, managing cross-border data transfers, and updating third-party vendor agreements in a secure deal room. Delays in addressing these issues can lead to fines up to $25 million or 4% of global revenue under laws like Quebec's Law 25.
Quick Tips to Avoid Mistakes:
- Audit Policies: Identify conflicts between the acquiring and acquired companies’ privacy terms.
- Secure Consent: Obtain explicit opt-in consent for any changes to how inherited data is used.
- Update Vendors: Ensure third-party processors meet your privacy standards.
- Notify Customers: Clearly communicate any privacy policy updates.
- Train Staff: Educate employees on new privacy obligations and systems.
Neglecting privacy updates is a costly mistake. Addressing these issues early ensures smoother integrations and compliance. Professional acquisition consultation services can help navigate these complex privacy transitions.
10 Privacy Policy Mistakes to Avoid After Company Acquisitions
Navigating Data Privacy Challenges in Mergers and Acquisitions

sbb-itb-a3ef7c1
Challenges in Updating Privacy Policies After Acquisitions
When companies merge, the data practices of the acquired company don’t just vanish - they come along for the ride. The FTC has made it clear: buying a business means inheriting its privacy commitments, and those commitments don’t disappear just because ownership changes hands. If the acquired company’s privacy policy promised stricter protections than your own, you’re now bound by those terms. Changing how that data is handled? That’ll likely require opt-in consent from every individual affected, which can be a logistical nightmare. This creates a breeding ground for potential policy conflicts.
These conflicts can be tricky to navigate. Let’s say the target company’s practices are weaker than yours - like storing unencrypted credit card data. Integrating their systems too quickly could expose your operations to vulnerabilities. On the flip side, if their privacy policy is more rigorous than yours, you’re left with two tough options: either upgrade your entire infrastructure to meet their standards or keep their data isolated indefinitely to avoid breaching those original terms. Neither path is easy - or cheap. Addressing these differences quickly is crucial to maintaining both legacy and current privacy standards.
Cross-border data transfers bring even more headaches. For example, transferring data from EU customers to the U.S. requires strict compliance with frameworks like the EU‑U.S. Data Privacy Framework or Standard Contractual Clauses. Experts caution against delaying these measures, as doing so could increase risks and regulatory exposure. These international complications only add to the challenges of integrating systems.
Liabilities don’t stop at policy conflicts. Acquirers can also inherit vulnerabilities or even breaches that existed before the deal closed. To minimize risk, it’s often best to keep the acquired systems separate until a thorough risk assessment is complete. However, this approach can frustrate teams eager to move forward with integration and unlock operational efficiencies.
Regulatory scrutiny ramps up when customer databases change hands. In asset-only deals, the FTC and state Attorneys General often require the buyer to stay in the same line of business as the seller to uphold original privacy promises. A key example of this is the Toysmart bankruptcy case, where the FTC blocked the sale of a customer database because it violated the company’s promise to never share customer information. This led to the creation of the "Toysmart Principles", which still influence how such transactions are handled today. Aligning privacy practices with regulatory standards is not just a legal requirement - it’s a cornerstone of responsible post-acquisition privacy management.
1. Not Updating Privacy Policies for Combined Data Practices
Integration of Data Practices Across Entities
When two companies merge, their data practices don’t automatically align. Acquirers often assume they can extend their own privacy policy to the acquired data without making necessary adjustments. This assumption can lead to legal complications. According to FTC regulations, the original privacy promises made to users remain enforceable.
The situation becomes even trickier when the acquired company’s privacy policy offers stricter protections than yours. In such cases, you’re left with two options: upgrade your data handling systems to meet their higher standards, or get explicit consent from each individual before applying your less restrictive terms to their data. A notable example is Facebook’s acquisition of WhatsApp in February 2014. By August 2016, WhatsApp updated its privacy policy to share customer data with Facebook, sparking an FTC warning. The regulator reminded both companies that they must honor the original promises made to users, particularly WhatsApp’s assurance that it wouldn’t share data for marketing without consent. This highlights the challenges of compliance when privacy protections differ between entities.
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
Regulations like GDPR enforce strict rules on how acquired data can be used. Under GDPR’s "purpose limitation" principle, data must only be used for the purposes it was originally collected for. For example, if the acquired company gathered email addresses solely for order confirmations, you can’t suddenly repurpose them for cross-platform marketing campaigns. Similarly, the FTC views it as deceptive to retroactively apply a less restrictive privacy policy to data collected under stricter terms, without obtaining user consent.
After an acquisition, buyers must take inventory of all tracking tools, such as chatbots, session replays, and cookies, to ensure compliance. The structure of the deal also impacts privacy obligations. For those navigating these complexities, using a tech-enabled acquisition platform can help streamline the due diligence process. In stock purchases, the buyer typically inherits all past privacy liabilities. On the other hand, in asset sales, transferring data may face stricter regulatory scrutiny, especially if the original privacy policy didn’t explicitly permit such a transfer.
Timeliness and Thoroughness of Updates
Updating privacy policies post-acquisition isn’t just a formality - it’s essential to maintain the integrity of user consent. It’s crucial to identify data sources tied to each version of the privacy policy to avoid mixing data with varying consent levels or restrictions. The FTC cautions:
Simply revising the language in a privacy policy or user agreement isn't sufficient because existing customers may have viewed the original policy and may reasonably assume it's still in effect.
Past regulatory actions underscore the importance of clear communication and obtaining proper consent before transferring customer data.
2. Ignoring Data Transfer Consent Requirements from Target Company
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
When acquiring a company, the privacy commitments made by the target company don't vanish - they remain legally binding. This can make navigating the consent process tricky.
Take the "Toysmart Principles" as an example. These came about after the FTC sued Toysmart in May 2000 for trying to sell its customer database despite promising customers their data wouldn’t be shared. If the target company’s privacy policy restricted data sharing, you’re required to get explicit opt-in consent from consumers before using their data in new ways.
Under GDPR, data transfers need a valid legal basis. Many companies lean on "legitimate interest" when planning integrations, but transferring sensitive data - like health records or religious details - requires explicit consent. Asset sales, in particular, face closer scrutiny than stock purchases because transferring data under restrictive conditions can violate the original privacy commitments. This makes consent a critical factor in how acquired data is integrated, which ties into the next point.
Integration of Data Practices Across Entities
Consent issues are just the beginning - integrating data practices between entities adds another layer of complexity. If the target company’s privacy policies offered stricter protections than your current practices, you’ll need to adjust. This could mean upgrading your data handling practices or segregating the acquired data until you secure individual consent to apply your terms.
To navigate this, start by auditing the target company’s previous privacy policies. Look for restrictive language and decide whether to align your practices with stricter standards or keep the data separate until you get explicit consent. During due diligence, establish clear data protection agreements to ensure the shared data is used strictly for the transaction.
Timeliness and Thoroughness of Updates
The importance of timely updates can’t be overstated. The FTC has repeatedly emphasized that acquisitions don’t override the original privacy promises made to consumers. As the FTC Business Blog puts it:
One company's purchase of another doesn't nullify the privacy promises made when the data was first collected. - FTC Business Blog
When making changes to pre-acquisition data, you’re required to get explicit opt-in consent. For post-acquisition updates, providing clear notice with an opt-out option might suffice. Mixing up these requirements could lead to regulatory penalties, including fines as high as $25 million or 4% of worldwide turnover under laws like Quebec’s Law 25.
3. Missing Third-Party Vendor Privacy Alignment After Acquisition
Integration of Data Practices Across Entities
When a company acquires another, it doesn’t just gain assets and customers - it also inherits a network of third-party vendors. These vendors often have their own data practices, which may not align with the acquiring company’s privacy policies. Esther Arokun from Seattle University School of Law highlights this challenge:
As companies consolidate, they inherit not only assets and liabilities but also vendor relationships that may introduce privacy vulnerabilities.
The issue arises when the acquired company’s vendors process customer data under terms that conflict with your privacy promises. If your policy guarantees protections that these vendors don’t uphold, the FTC could interpret this as an "unfair or deceptive act". This misalignment creates compliance risks that demand immediate attention.
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
Technologies like chatbots, session replays, and tracking cookies often come under scrutiny, facing legal challenges under regulations like the CCPA and CIPA. Under GDPR, companies are required to have written agreements with data processors, ensuring they operate strictly under the company’s instructions. Similarly, the CCPA mandates specific contract provisions to govern data sharing with third-party processors. If the acquired company’s vendor agreements don’t meet these regulatory standards, you could face compliance issues as soon as the acquisition closes.
The first step to addressing these risks is reviewing and updating vendor agreements to include the necessary privacy clauses.
Timeliness and Thoroughness of Updates
Dealing with these challenges starts with a detailed inventory of the target company’s technology. Before finalizing the deal, conduct a comprehensive audit of their digital assets to identify tools like tracking technologies, chat systems, and recording software. Kathryn M. Rattigan from Robinson & Cole LLP stresses the importance of early action:
For buyers, robust due diligence can prevent expensive surprises shortly after closing.
Once you’ve identified the vendors, update their contracts to include the required privacy safeguards. It’s also important to estimate the costs of these updates upfront. If any vendors fail to meet your standards, their technologies should be disabled immediately to avoid liability.
Effective Communication with Stakeholders
After updating contracts and completing audits, clear communication with internal teams is critical. One common mistake in mergers and acquisitions is excluding privacy and cybersecurity specialists from the integration process. Liisa M. Thomas and Snehal Desai from Sheppard Mullin explain:
In many deals, the privacy and cybersecurity team is not involved in the integration process. Or, a different team handles these steps.
Involve privacy experts early in the due diligence phase to map out how vendor data will be integrated. This proactive approach helps identify potential conflicts early on and ensures that data flows remain compliant.
4. Delaying Customer Notification of Policy Changes
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
Keeping customers informed about updates to privacy policies is a crucial part of any post-acquisition process. When a company is acquired, it takes on the privacy commitments of the acquired business. According to the FTC Act, failing to honor these original commitments can be considered deceptive behavior. If you plan to modify how data collected before the acquisition is used, you must secure clear, affirmative opt-in consent from the affected customers. For data collected after the acquisition, clear notice and an opt-out option must be provided. These steps ensure transparency and compliance during the integration phase.
European Union laws add further requirements. Data subjects must be notified about any transfer of their data to a third party at the time of the transfer. In the United States, California's enforcement of the CCPA and CIPA has led to lawsuits against companies that fail to disclose tracking technologies or obtain proper consent. The consequences can be severe. For instance, Quebec's Law 25 allows penalties of up to $10 million or 2% of global turnover for privacy violations.
Timeliness and Thoroughness of Updates
Acting quickly on privacy updates is essential to avoid regulatory penalties. After Facebook acquired WhatsApp in February 2014, the FTC issued a warning: WhatsApp had to continue honoring its original privacy promises unless it obtained explicit opt-in consent from users. When WhatsApp later revised its policy in August 2016 to share user data with Facebook, users were given a 30-day window to opt out.
The Marriott-Starwood case highlights the dangers of delays. A security vulnerability in Starwood's network went unnoticed for four years, including two years after Marriott acquired the company. This breach compromised 339 million records. The Office of the Privacy Commissioner of Canada noted that Marriott, as the acquiring party, was responsible for ensuring Starwood's data security from the moment of integration.
Effective Communication with Stakeholders
Updating a privacy policy isn't enough on its own. The FTC has made it clear:
Simply revising the language in a privacy policy or user agreement isn't sufficient because existing customers may have viewed the original policy and may reasonably assume it's still in effect.
To ensure compliance and maintain trust, notifications must be clear and visible. This means using direct communication methods like email updates, dashboard alerts, or other prominent notices - not just quietly updating the "last revised" date on a webpage. Clear communication helps customers understand the changes and exercise their rights, making it a key part of the integration process.
5. Ignoring GDPR and CCPA Compliance When Harmonizing Policies
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
When acquiring a company, you’re not just merging operations—leveraging technology in business transactions—you’re also inheriting two distinct sets of privacy regulations. The GDPR requires a clear legal basis for every data processing activity, such as "legitimate interest", "consent", or "performance of a contract". On the other hand, the CCPA emphasizes transparency, requiring businesses to provide notice and allow consumers to opt out of data sales or sharing. These differing frameworks can make aligning privacy policies a challenging task.
Integration of Data Practices Across Entities
Under GDPR, data can only be used for the purpose it was originally collected. For example, if customer emails were gathered solely for order confirmations, you can’t use them later for marketing without obtaining new consent.
Cross-border data transfers bring even more complexity. GDPR imposes strict rules on moving personal data outside the European Economic Area (EEA) to countries not deemed "adequate", such as the United States. To comply, companies must use Standard Contractual Clauses (SCCs) or rely on approved frameworks like the Data Privacy Framework to ensure legal data transfers.
| Compliance Area | GDPR Requirement | CCPA/U.S. Requirement |
|---|---|---|
| Legal Basis | Requires legitimate interest, consent, or contract | Based on notice and opt-out rights |
| Policy Changes | Material changes may require new consent | Material changes require opt-in consent |
| Data Transfer | Needs SCCs or adequacy for cross-border | Requires notice and opt-out for asset sales |
| Website Tracking | Explicit consent required for non-essential cookies | Must disclose IP addresses and tracking tech |
Timeliness and Thoroughness of Updates
Failing to align privacy policies can lead to severe penalties. For instance, under Quebec's Law 25, organizations face fines of up to $10 million or 2% of global revenue for administrative violations. Serious offenses can result in penalties as high as $25 million or 4% of worldwide turnover. These are not hypothetical risks - enforcement is active.
Before harmonizing policies, conduct a thorough audit of the target company’s website tracking technologies. In California, CCPA classifies identifiers like IP addresses and browsing history as personal information. This has sparked lawsuits over tools like chatbots and session replay technologies, often referred to as "trap and trace" litigation. Acting quickly to identify and address compliance gaps can prevent costly legal issues down the road.
Ready to Make Your Next Move?
Whether you're buying, selling, or investing — Clearly Acquired gives you the tools, data, and support to close with confidence.
6. Insufficient Documentation of Data Mapping Across Entities
Integration of Data Practices Across Entities
When acquiring a business, you’re not just taking over its customer database - you’re also inheriting every privacy commitment it ever made. Without proper data mapping, it becomes difficult to trace how and when data was collected, exposing you to legal risks. For instance, if the acquired company updated its privacy policy multiple times, various portions of the database could be subject to different restrictions.
The Federal Trade Commission (FTC) has made its stance clear:
One company's purchase of another doesn't nullify the privacy promises made when the data was first collected.
What does this mean in practice? If the acquired company assured customers their email addresses wouldn’t be shared with third parties, you can’t suddenly use that data for marketing campaigns without obtaining fresh consent. Proper data mapping helps ensure you honor these legacy promises and simplifies future compliance efforts.
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
Accurate data mapping isn’t just about respecting past promises - it’s essential for staying on the right side of privacy laws. Start by taking inventory of all tracking tools on the target’s website. This includes chatbots, session replays, and third-party analytics. Why? Because failing to do so could lead to hefty penalties. For example, in 2025, class-action lawsuits under the California Invasion of Privacy Act surged, targeting companies that used these technologies without proper consent.
Cross-border data transfers add another layer of complexity. If the acquired company processes personal data from EU residents, you’ll need to confirm that their data transfer certifications, like the Data Privacy Framework, are up to date. Additionally, ensure mechanisms like Standard Contractual Clauses are in place to meet compliance requirements .
A cautionary tale: In September 2022, Canada’s Office of the Privacy Commissioner (OPC) published findings on Marriott International’s 2018 data breach. The breach originated from Starwood Hotels’ systems back in 2014 - two years before Marriott acquired the company. The breach went undetected for four years, impacting up to 339 million records. The OPC concluded that Marriott, as the purchaser, bore responsibility for the vulnerabilities in Starwood’s systems and should have conducted rigorous security testing before integrating the data.
Timeliness and Thoroughness of Updates
Before transferring any personal data, it’s crucial to establish a formal agreement that limits its use exclusively to integration planning. You should also map data according to the applicable privacy policy version, audit agreements with third-party vendors, and ensure compliance with cross-border data transfer laws. Taking these steps can help prevent regulatory headaches and protect your organization from costly mistakes.
7. Keeping Outdated Consent Mechanisms from Acquired Business
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
When acquiring a business, you often inherit older consent mechanisms - like outdated cookie banners or opt-in checkboxes - that may no longer meet current regulatory standards. The Federal Trade Commission (FTC) has emphasized that an acquisition doesn’t erase the original privacy commitments made when the data was collected. Relying on these outdated tools can lead to violations under Section 5 of the FTC Act, which prohibits deceptive practices.
In California, the risks are even greater. Tools like chatbots, session replay technologies, and cookies that lack proper consent mechanisms can lead to lawsuits under the California Invasion of Privacy Act (CIPA) and the California Consumer Privacy Act (CCPA). Similarly, under the General Data Protection Regulation (GDPR), businesses must obtain clear and specific consent for activities like targeted advertising - pre-checked boxes or vague language won’t cut it. To navigate these challenges, an immediate audit of all consent tools is crucial. Utilizing specialized buyer tools can streamline this due diligence process.
Integration of Data Practices Across Entities
Updating consent tools isn’t just about meeting legal requirements - it’s also about maintaining user trust. Start by conducting a thorough audit of the acquired company’s tracking technologies, such as chatbots, analytics tools, and data-collecting scripts. For instance, if the company’s website used a generic banner like “By using this site, you agree to cookies,” and your jurisdiction requires explicit opt-in consent, those mechanisms need to be replaced immediately. History shows that failing to update these tools can lead to significant penalties.
It’s equally important to honor opt-out requests made under the acquired company’s original policies. A notable example is the Borders bankruptcy sale to Barnes & Noble, where the court mandated that Borders’ prior opt-out requests be respected - unless those customers were already Barnes & Noble users who hadn’t opted out. If aligning your practices with the acquired company’s original consent standards proves too complex, you might need to isolate the acquired data to ensure it isn’t used improperly.
Timeliness and Thoroughness of Updates
Speed matters when updating consent mechanisms. Changing the wording of a privacy policy alone isn’t enough. The FTC has cautioned that customers may reasonably believe the original terms still apply unless they’re explicitly informed otherwise. When revising privacy terms, provide clear and prominent notice - don’t bury updates in hard-to-find sections of your website.
Additionally, review all vendor agreements to confirm they align with the updated consent levels promised to users. If vendors process data in ways that users didn’t agree to, your business could face liability. Ensuring these updates are both timely and thorough is key to avoiding compliance risks and maintaining trust with your user base.
8. Not Auditing Digital Assets for Privacy Policy Conflicts
Integration of Data Practices Across Entities
When acquiring a company, it’s not just about merging operations or customer bases - it’s also about inheriting digital assets like tracking technologies, cookies, chatbots, and analytics tools. These assets often come with their own set of privacy promises, which may conflict with your current practices. Overlooking these mismatches can lead to serious problems.
Conduct a thorough audit of all digital tools used on the acquired company’s platforms. This includes technologies like session replay tools that track user behavior, chat widgets that log IP addresses and conversations, and third-party analytics plugins. Compare how each tool operates against the acquired company’s historical privacy policies and your own. For instance, if the acquired company previously assured users that it would "never share data with third parties", but your systems routinely send visitor data to advertising platforms, this discrepancy could attract regulatory attention. A detailed audit is crucial to ensure that inherited practices align with your compliance standards.
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
Skipping this audit isn’t just risky - it could lead to regulatory penalties. Agencies like those enforcing GDPR or CCPA hold acquiring companies accountable for ensuring that inherited systems and databases meet privacy and security requirements. Failing to address these issues before integrating the acquired assets can result in costly consequences.
Timeliness and Thoroughness of Updates
Acting quickly is key. Kathryn M. Rattigan of Robinson & Cole LLP emphasizes the importance of proactive due diligence:
Website privacy litigation isn't going away, and regulatory scrutiny will only increase. For buyers, robust due diligence can prevent expensive surprises shortly after closing.
If your audit uncovers high-risk practices - like "trap-and-trace" technologies - take immediate action. This might mean requiring the seller to deactivate these tools or disclose their use clearly. If aligning the acquired company’s practices with your standards is too expensive or complicated, calculate the remediation costs before closing the deal. Alternatively, consider isolating the acquired data to minimize future liabilities. Taking these steps early can save your organization from regulatory headaches down the road.
9. Poor Communication of New Privacy Terms to Stakeholders
Effective Communication with Stakeholders
Updating a privacy policy isn’t just a box to check - it’s a legal and ethical responsibility, especially after an acquisition. The Federal Trade Commission (FTC) emphasizes this point:
Simply revising the language in a privacy policy or user agreement isn't sufficient because existing customers may have viewed the original policy and may reasonably assume it's still in effect.
Take the example of Facebook’s acquisition of WhatsApp in 2014. The FTC warned both companies about maintaining user trust. When WhatsApp updated its privacy policy in August 2016 to share user data with Facebook, it faced backlash from regulators, privacy advocates, and users. The company allowed users only 30 days to opt out of the data-sharing arrangement, which drew significant criticism. This scenario highlights the importance of proactive and transparent communication to meet consent requirements under laws like GDPR and CCPA.
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
Failing to honor a company’s original privacy commitments can be considered a "deceptive act" under Section 5 of the FTC Act. If you’re making material changes to how pre-acquisition data is handled, affirmative opt-in consent is usually required from those affected. For data collected after the acquisition, companies must provide clear notice and an opt-out option. These steps are not just legal necessities - they're essential for maintaining trust and avoiding compliance issues.
Timeliness and Thoroughness of Updates
When updating privacy terms, timing and clarity are everything. Use multiple channels - like emails, website banners, pop-ups, or dashboards - to ensure stakeholders are informed immediately. Under European Union regulations, data subjects must be notified of any transfer of their personal information no later than the time the transfer takes place. Thorough documentation of these efforts is critical to reduce regulatory risks.
Consider the case of RadioShack’s bankruptcy sale. The company had promised its customers that their personal information wouldn’t be sold. When the sale occurred, 38 state Attorneys General required the buyer to notify customers and offer opt-out options. This serves as a reminder: clear, timely communication isn’t just good practice - it’s non-negotiable.
10. Skipping Privacy Training for Staff After Acquisition
Integration of Data Practices Across Entities
When one company acquires another, it’s not just about merging assets or operations - employees also inherit the responsibility of managing both their own data and any vulnerabilities tied to the acquired entity. Take the Marriott-Starwood case, for example: failing to train staff on inherited systems left pre-existing vulnerabilities exposed.
It’s not enough to align technical systems; your team needs to be informed and trained to handle these inherited risks effectively. This means offering targeted training on how to manage acquired data. Employees must understand when it’s appropriate to isolate systems versus when integration is safe. Those handling sensitive information - like payroll, medical records, or customer data - should be taught standardized privacy and security protocols to ensure consistency and compliance.
As privacy experts from Sheppard Mullin Richter & Hampton point out:
In many deals, the privacy and cybersecurity team is not involved in the integration process... Issues that might arise include understanding the data and processes that will be needed post integration, and the personnel who can help.
Compliance with Privacy Regulations (e.g., GDPR, CCPA)
The risks of non-compliance with privacy regulations are steep. For instance, Quebec's Law 25 imposes administrative penalties of up to $10 million or 2% of worldwide revenue, with more severe violations resulting in fines as high as $25 million or 4% of global turnover. Similarly, California is actively enforcing the CCPA and the California Invasion of Privacy Act, particularly in areas like chatbots, session replays, and cookie tracking.
Acquiring a company doesn’t erase its prior privacy obligations. A notable example is the FTC’s 2014 warning to Facebook and WhatsApp: failing to honor WhatsApp’s original data commitments would be considered a deceptive act under the FTC Act. To avoid such pitfalls, training should include how to review and manage inherited consent records so they align with current regulations. Without proper staff training, compliance risks skyrocket, and efforts to unify privacy practices post-acquisition may falter.
Timeliness and Thoroughness of Updates
Making privacy training a priority after an acquisition is a critical step in your post-acquisition workflow. This training should kick off immediately - ideally before any data integration - to minimize the risk of breaches or violations.
Running tabletop exercises to test updated incident response plans can further prepare your team for potential challenges. Additionally, cross-training M&A and privacy teams using established playbooks can empower employees to spot privacy risks on their own. This approach ensures everyone understands the specific objectives of the acquisition and how data practices will be aligned.
How Clearly Acquired Can Help with Acquisitions
Clearly Acquired simplifies the often-complicated process of post-acquisition integration by tackling privacy compliance challenges head-on. Acquisitions can bring significant privacy risks, but this AI-powered platform takes a proactive approach. It conducts automated gap analyses to identify outdated notices, policy inconsistencies, and missing disclosures early in the process. This helps mitigate what experts call "privacy time bombs" before they become costly issues.
The platform also provides a comprehensive map of regulatory requirements across various jurisdictions. Whether you're navigating GDPR, CCPA (applicable to businesses generating over $25 million in revenue and handling California resident data), or newer regulations in states like Virginia, Colorado, and Utah, Clearly Acquired offers clear, actionable guidance on the specific rules impacting your transaction. Notably, 96% of CIOs have reported that technology due diligence uncovered critical issues or opportunities that significantly influenced M&A outcomes.
In addition to policy reviews, Clearly Acquired ensures third-party vendor relationships align with your privacy standards. It streamlines data inventory and mapping processes, which are essential for managing data subject access requests after the deal closes. For cross-border transactions, the platform evaluates safeguards for transferring personal data outside the EEA or UK, ensuring compliance with GDPR's stringent rules on international data flows.
To further protect sensitive information during due diligence, Clearly Acquired offers secure data rooms, automated NDAs, and centralized deal management hubs. Its advisory services also flag conflicting policy restrictions, helping to harmonize privacy practices. As Paul A. Chandler of Mayer Brown LLP cautions, delaying these measures can significantly increase risks.
Whether you're acquiring your first company or expanding through multiple deals, Clearly Acquired equips you with the tools to navigate privacy compliance confidently. From due diligence to integration, these solutions fit seamlessly into your acquisition strategy, ensuring smooth transitions and consistent compliance every step of the way.
Conclusion
Updating privacy policies after an acquisition isn’t optional - it’s a legal and practical necessity from day one. As the Federal Trade Commission puts it:
One company's purchase of another doesn't nullify the privacy promises made when the data was first collected.
When acquiring a company, you’re not just taking on its assets - you’re also inheriting its legal obligations tied to data privacy.
Delaying these updates can lead to serious consequences. Companies have faced breaches and deceptive practice claims for failing to act promptly, as highlighted in several high-profile cases. The financial fallout can be steep. Under Quebec's Law 25, organizations can face penalties up to $10 million or 2% of global revenue, with more severe violations reaching $25 million or 4% of global revenue. Beyond these fines, outdated consent mechanisms and tracking technologies can trigger lawsuits under laws like the CCPA and CIPA.
To avoid these risks, companies should take immediate steps: isolate legacy systems, revise privacy policies, update consent mechanisms, and secure affirmative opt-in consent for any new data uses. Crucially, privacy and cybersecurity experts should be involved during the due diligence phase - not after the deal is done - to identify and address risks before they become liabilities.
Ultimately, timely and effective updates to privacy policies are about more than just compliance. They’re key to maintaining customer trust and supporting long-term growth. Clear communication about policy changes, coupled with thorough documentation of data practices, is essential in today’s regulatory landscape. Privacy compliance isn’t just about avoiding penalties - it’s a cornerstone for building trust and ensuring sustainable success after every acquisition.
About the author
Principal & CEO/CIO
Samson Jagoras has 15+ years across finance, real estate, and business acquisitions. He began his career as a Futures & Commodities broker and later served as Chief Strategy Officer of an INC 500 marketing and technology firm, helping scale revenue from $1M to over $100M. Today he buys, builds, and advises a portfolio of companies with a focus on M&A, capital allocation, and operational strategy.