SMB Breach Costs and M&A Risk: 2026 Summary
How SMB cyber breaches affect M&A: $120K–$1.24M typical costs, 22–23 day downtime, extortion trends, and valuation/financing impacts.
 Samson JagorasPrincipal & CEO/CIOSeptember 19, 2026
Get matched with the right lender for your business
Compare offers from our vetted network. Pre-qualify in minutes — no impact to your credit.
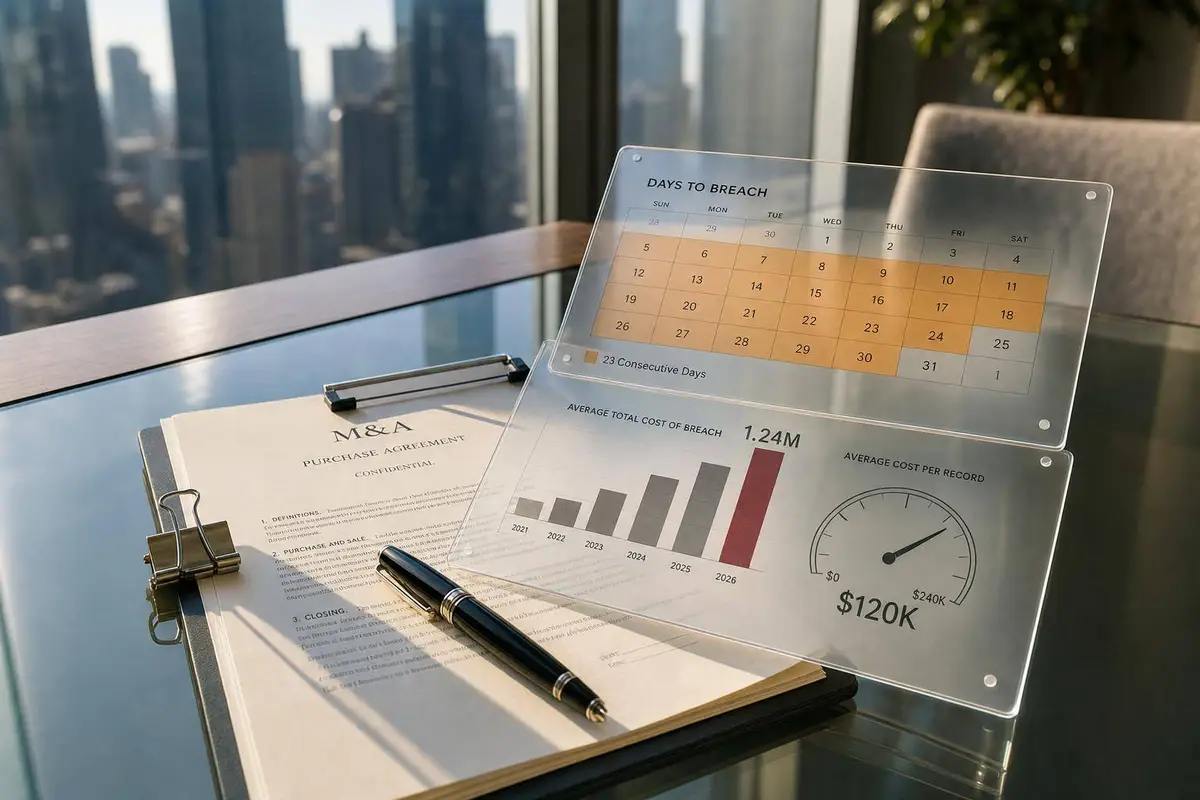
Cyber risk now changes deal math. In 2026, a small-business breach can cost anywhere from $120,000 to $1.24 million in many deals, while harsher cases can hit 7% of annual revenue.
If I were sizing up an SMB acquisition, I’d keep four things front and center:
- Breach cost: many SMB incidents land in the $120,000 to $1.24 million range
- Downtime: ransomware recovery often takes 22–23 days, and 34% of victims need more than a month
- Extortion: 87% of ransomware group activity now includes double extortion
- Attack paths: most SMB breaches trace back to system intrusion, social engineering, and web app attacks
- Deal effect: cyber issues can lead to 8%–25% valuation cuts, tighter debt terms, or post-close cash needs
This comes down to a simple deal question: if systems go down, data gets taken, or email is hijacked, what happens to EBITDA, cash flow, and debt service?
A few points stand out fast:
- A ransom payment is often not the largest cost
- Lost sales, legal work, customer loss, and recovery work can cost more than the attack itself
- Weak MFA, exposed remote access, bad backups, and poor logging are common warning signs
- If a target has known gaps, I’d put the cost into price, structure, or the 100-day budget
Here’s a quick snapshot:
| Area | What the data says | Why it matters in a deal |
|---|---|---|
| Breach cost | $120,000–$1.24 million for many SMBs | Can cut cash reserves and post-close earnings |
| Severe stress case | Up to $3.31 million for firms under 500 employees | Useful for hard-case underwriting |
| Ransomware downtime | 22–23 days on average | Hits revenue, billing, and loan coverage |
| BEC loss | About $129,196 per incident | Direct cash loss and working-capital hit |
| Valuation effect | 8%–25% adjustments in some deals | Can change price and structure |
So if I were reading this for deal work, my takeaway would be simple: test cyber risk the same way you test customer concentration, margins, and debt capacity. That means pricing the downside, checking the controls, and setting aside money to fix what’s broken.

SMB Cyber Breach Costs & M&A Risk: 2026 Key Data Points
The Biggest Cybersecurity Trends SMBs Are Facing in 2026

sbb-itb-a3ef7c1
2026 Breach-Cost Benchmarks for U.S. SMBs
For most U.S. SMBs, a practical underwriting range is $120,000 to $1.24 million per incident. IBM’s own size-band data puts the average for businesses with fewer than 500 employees at about $3.31 million, which makes it a useful stress-test benchmark for data-heavy or regulated targets.
What matters for buyers is how that range shifts with company size:
| Size Band | Realistic Breach-Cost Range | Primary Cost Drivers |
|---|---|---|
| Micro-SMB (under 50 employees) | $120,000–$250,000 | Incident response, basic legal work, short downtime |
| Core SMB (50–250 employees) | $250,000–$750,000 | Legal, notification, remediation, downtime |
| Upper SMB (250–500 employees) | $750,000–$1.24 million | Regulatory exposure, extended outage, customer churn |
Across SMBs, detection often takes 30–90 days, containment 7–21 days, and full recovery 30–90 days.
What Is Included in Breach Cost
Breach cost is more than IT cleanup. That’s where many buyers get caught off guard.
The full picture usually includes forensic investigation, incident response, and technical remediation, plus outside legal counsel for breach notification and regulatory reporting. It also includes state-law-required notification and credit monitoring, infrastructure hardening, and cyber insurance retentions and coverage gaps. Then come the indirect costs: lost sales during downtime, customer churn, and management time pulled into crisis response instead of day-to-day operations.
The costs most likely to show up after close are often the least obvious ones. Hidden legal duties and unfinished prior remediation are common examples. A target may have gone through a ransomware event informally, with no outside counsel, no regulatory reporting, and no written record of remediation. That can leave the new owner dealing with retroactive notification duties, regulator questions, or customer contract fights later on. Insurance issues can make things worse. Post-close policy reviews sometimes show that coverage lapsed or that earlier incidents were never disclosed, which can lead to higher retentions or denied claims.
Why Containment Time Drives Total Loss
Speed matters. A lot.
IBM’s 2024 data puts the average breach lifecycle at 258 days - about 194 days to identify and 64 days to contain. Breaches that last more than 200 days cost about $1.1 million more than faster-contained incidents. For an SMB, that difference isn’t just a budgeting issue. It can be the line between a painful event and a business-threatening one.
For buyers, this turns into plain diligence questions. A target with structured logging, solid backup hygiene, endpoint monitoring, and a written incident-response plan is in a better position to detect and contain an issue than a company relying on informal IT practices. Shorter timelines usually mean less data taken, a smaller legal and notification burden, fewer incident-response hours, and less disruption to the business.
When a target can’t answer basic questions about detection tools or incident-response playbooks, that tells you something. It points to both weak security discipline and larger downside risk. And when containment drags on, downtime tends to stretch too, which is where ransomware losses start to snowball.
Ransomware, Downtime, and Extortion Trends Hitting Small Businesses
When breach costs come from ransomware, the damage isn't limited to cleanup. The bigger hit is often business disruption plus extortion. Ransomware turns a security gap into direct cash loss, downtime, and liability that can follow the deal after close. Attackers don't just lock systems anymore. They also steal data and stack threats to pressure a company into paying.
Double extortion - where attackers encrypt systems and exfiltrate sensitive data - is now standard practice in about 87% of ransomware group operations. Triple extortion adds another layer, such as DDoS threats or direct outreach to customers and partners, and shows up in about 34% of attacks. For buyers, that changes the risk picture. A target may have strong backups and still face regulator attention, customer claims, and brand damage tied to stolen data. Those problems can end up on the new owner's desk after close.
Recovery Costs Usually Exceed the Ransom
The ransom demand is often NOT the biggest expense. Sophos's 2025 data put average recovery costs, excluding the ransom, at about $1.53 million, while median ransom payments were roughly $139,000 to $150,000.
Why is the gap so wide? Because the money goes everywhere at once: system rebuilds, lost staff output, customer disruption handling, legal counsel, and regulatory notice work. For SBA- or bank-financed deals, this is a working-capital problem as much as an IT problem. A post-close budget should spell out reserves for incident response retainers, faster hardware and software replacement, and customer retention spending, all stated in dollars and matched to the target's size and sector.
Downtime Is an Underwriting Issue, Not Just an IT Issue
Average ransomware downtime now runs 22–23 days, and 34% of victims need more than a month to recover. That's not a minor tech headache. It's weeks of lower revenue, delayed billing, and a leadership team pulled away from running the business.
And that downtime doesn't hit every company the same way. A law firm, a medical practice, and a distributor can all lose a month, but the pain shows up in different places.
| SMB Profile | Operational Impact | M&A Risk |
|---|---|---|
| Services / professional firms | Missed appointments, delayed invoicing, stalled projects | Delayed billing, covenant pressure |
| Healthcare practices | Canceled visits, billing delays, insurer delays or denials | Lost visits, regulatory exposure |
| Manufacturing / distribution | Halted production, missed shipments, margin pressure | Contract performance risk, working-capital strain |
| Multi-site retail / hospitality | POS outages, lost card transactions, chargebacks | Brand damage, customer loss |
Because downtime flows straight into revenue, margin, and debt service capacity, lenders and equity sponsors treat it as an underwriting variable, not a side note. If a target can't show its recovery time objectives, or hasn't tested backups in the recent past, a lender has little choice but to stress-test the deal harder. IBM's 2024 data backs this up: 75% of the increase in breach costs is driven by lost business and post-breach response, not technical containment. That's the anchor point for deal underwriting.
The next question is which attack patterns most often create that exposure.
Attack Patterns and Vulnerability Signals Buyers Should Look For
Three attack patterns show up again and again in SMB breaches: System Intrusion, Social Engineering, and Basic Web Application Attacks. Together, they make up about 92–96% of breaches in small businesses. That narrows the field for buyers. Instead of trying to review every possible threat, they can focus on a small set of repeat issues that tend to drive loss.
Ransomware often grows out of these same patterns. But in SMB deals, BEC and credential theft can be just as damaging, and sometimes worse. FBI IC3 recorded 21,442 BEC complaints in 2024 and $2.77 billion in reported losses, which works out to about $129,196 per incident. BEC also drives a large share of hidden losses, with about ten BEC events for every ransomware incident across insurance and threat-intel portfolios. For buyers, that matters because these attack patterns help set the right depth of diligence and shape how much risk should sit in the purchase price.
Credential Risk and the Human Element
Stolen credentials are the most common initial attack vector globally, making up about 16% of breach entry points in IBM's 2024 data. At the same time, many SMBs still lack basic protection. As of 2024, only about 35% of SMBs worldwide have implemented MFA, down from 46% two years earlier. And about 80% of breaches involve stolen credentials used without MFA, which means one stolen password can become a company-wide problem very fast.
For finance teams, this hits close to home. It isn't some distant IT issue. It can mean misdirected payments, account takeover, and direct working-capital loss.
Buyers should look for a few plain controls:
- Out-of-band verification for vendor banking changes and payroll updates
- Dual approval for large wire transfers
If those controls don't exist, the fraud-loss exposure should show up in the quality-of-earnings review.
Technical Gaps That Change Deal Risk
The clearest warning signs are familiar ones: unpatched perimeter devices, unsupported operating systems, weak backups, shared admin accounts that blur accountability, and incomplete logging. Sophos found that remote ransomware rose 50% in 2024 and 141% since 2022, often through exposed RDP or other internet-facing remote access.
Backups need extra scrutiny. Some incident responders have seen cases where a company's "backup" was actually just a live production share or a removable drive plugged into the infected server. In a crisis, that leaves no real recovery path. A buyer should ask for backup architecture diagrams, RPO/RTO targets, and proof of a recent restore test, not just a yes-or-no answer that backups exist.
Use the table below to connect each attack type to its root cause, business impact, and the proof a buyer should request. The goal isn't to build a giant threat list. It's to spot the issues that can change deal terms.
| Attack Type | Common Root Cause | Typical Business Impact | Diligence Signals to Request |
|---|---|---|---|
| Phishing / BEC | No MFA on email; no payment verification process | Wire fraud, misdirected payments, account takeover | Incident log, phishing simulation records, MFA coverage report |
| Ransomware via RDP/VPN | Exposed remote access, no MFA, weak credentials | Multi-week downtime, data loss, extortion | Remote-access inventory, MFA configs, backup restore-test evidence |
| Credential theft | Password reuse, no SSO, no credential leak monitoring | Account takeover, lateral movement, data exfiltration | Password policy docs, SSO usage, privilege review records |
| Vulnerability exploit | Unpatched firewalls, end-of-life OS or ERP | Network compromise, ransomware deployment | Vulnerability scan results, patch SLA reports, EOL software list |
| Backup failure | Single on-prem backup, no offsite or cloud copy | Extended downtime, forced ransom payment | Backup architecture diagram, RPO/RTO docs, last restore-test date |
| Incomplete logging | No SIEM or MDR, short log retention | Inability to scope breach, regulatory exposure | Log-management config, retention policy, third-party monitoring agreements |
When several of these gaps show up together - no MFA on remote access, an unsupported Windows Server, and backups that haven't been tested - a buyer should move beyond standard diligence and open a deeper technical review. That usually means a focused vulnerability assessment and a detailed admin-account inventory. Those combined signals should also feed into valuation, lender review, and the post-close cyber budget.
What the Data Means for Valuation, Financing, and Post-Close Budgets
Once diligence turns up cyber gaps, the next step is simple: put a dollar figure on them, decide where they sit in the deal, and pay for the fix in the 100-day plan. So the issue isn't whether cyber risk should be addressed. It's where that risk shows up in price, structure, and post-close spending.
How Buyers and Investors Should Reflect Cyber Risk in Price and Structure
Survey data from M&A professionals shows that 86% say a public breach at a target lowers acquisition price, and middle-market advisory data shows that material cyber issues have led to 8%–25% valuation adjustments. In cases where issues were missed during diligence, post-close value destruction has run $4 million to $8 million. The same math also affects how much debt a business can carry.
A practical way to handle this is to split issues into two buckets. If the gaps are fixable within 6 to 12 months, treat them as post-close budget items. That can mean EBITDA adjustments, working-capital reserves, or a 100-day remediation plan.
If the issues are more serious - like unresolved incidents, repeat credential compromise, or broken backups - they belong in the deal structure. In plain English, that usually means:
- Indemnities
- Escrows
- Holdbacks
Active breaches and regulatory investigations can justify a re-trade or even walking away. Major control gaps can support price cuts, escrows, or holdbacks. In lower-valued SMB deals, even the low end of that adjustment range can make or break the model. That's why lenders often treat cyber findings as underwriting inputs, not just footnotes from diligence.
How Lenders and Capital Partners View Weak Cyber Posture
Lenders tend to view weak cyber posture as cash-flow risk. Syndicated-loan data shows spreads increase by 4 to 13 basis points when cyber risk rises by one standard deviation, and insurance doesn't remove that pricing effect.
That same concern shows up across SBA-backed deals, bank debt, seller notes, and outside equity. The core question is straightforward: can this business keep servicing debt if email, billing, or operations are down for weeks?
When the answer looks shaky, lenders and capital partners may react in a few ways:
- Tighten leverage
- Ask for more diligence
- Make remediation a closing condition
Weak controls can also reshape the capital stack. A buyer may need to use more equity, ask for more seller rollover, or accept tighter post-close covenants.
Conclusion: A Simple Framework for SMB Cyber Risk in 2026 M&A
Price, debt, and remediation budgets should all reflect the same cyber exposure.
The data across this summary points in one direction: SMB breach events can create seven-figure losses, and downtime plus recovery often cost more than the ransom itself. That makes cyber posture a deal variable. It should affect diligence scope, purchase price, deal structure, financing terms, and the first-year operating budget.
A simple framework works best: identify the exposure, estimate the likely cost, decide whether it belongs in price or structure, and fund the fixes before they turn into a surprise. Modest, fixable gaps fit the post-close budget. Known but unresolved issues fit escrows and indemnities. Anything that puts cash flow or financing at risk is a reason to re-trade terms or walk away.
FAQs
How should I underwrite cyber risk in an SMB deal?
Cyber risk needs to connect straight to deal economics. For SMBs, attack exposure is high, and a breach can cost about $3.1M–$3.31M. That means 2026 underwriting should go past a surface-level IT check.
Buyers need deeper IT and security diligence, faster issue triage, and a clear post-close remediation budget. Put simply, if security gaps exist, the model should show what it will cost in time and money to fix them.
Weak controls can also justify stronger deal protections, such as escrow or tighter terms. That way, financing lines up with likely cash needs instead of best-case assumptions.
What cyber red flags matter most in diligence?
For SMB deals, cyber risk hits valuation and diligence head-on: 43% of cyberattacks target small businesses, and the average breach costs about $3.31 million.
Put your diligence focus on identity and access controls, backups and disaster recovery, and incident-response readiness. In plain terms, you want to know who can get into what, whether the company can restore systems if things go sideways, and how prepared the team is if an attack happens.
It also helps to treat ransomware and downtime as post-close budget items. That means folding remediation costs into financing assumptions and integration planning from the start, not after the damage is done.
When should cyber risk change price or deal terms?
Cyber risk should affect price or terms when diligence finds gaps that could lead to major cleanup costs, fines, downtime, or lost business value. That matters because 43% of attacks target SMBs, and average breach costs top $3.31 million.
Buyers should zero in on IT infrastructure during diligence, especially network security, identity controls, and data backups. If the review turns up material gaps, those issues should show up in valuation, financing, or post-close remediation planning.
Related Reading
Find the right lender for your business
Whether it's working capital, an SBA loan, or acquisition financing — we'll match you with the right capital partner.
About the author
Principal & CEO/CIO
Samson Jagoras has 15+ years across finance, real estate, and business acquisitions. He began his career as a Futures & Commodities broker and later served as Chief Strategy Officer of an INC 500 marketing and technology firm, helping scale revenue from $1M to over $100M. Today he buys, builds, and advises a portfolio of companies with a focus on M&A, capital allocation, and operational strategy.