AML Risks in M&A: 7 Compliance Red Flags
Seven AML risks to watch in M&A deals - KYC gaps, sanctions, weak monitoring and governance - and how to score, price, and remediate each one before close.
 Samson JagorasPrincipal & CEO/CIOJune 22, 2026
Buy a company with weak AML controls, and you may buy its old problems too. That can mean fines, lender pushback, closing delays, and post-close cleanup. One clear case: after its 2008 Wachovia deal, Wells Fargo later paid $160 million tied to inherited AML failures.
If I had to sum up the article in one line, it would be this: check AML risk before close, score it fast, and tie each issue to price, legal terms, or a fix plan. In small and mid-market deals, the weak spots are often simple but costly — missing KYC files, unclear ownership, thin screening, weak monitoring, poor governance, and messy records.
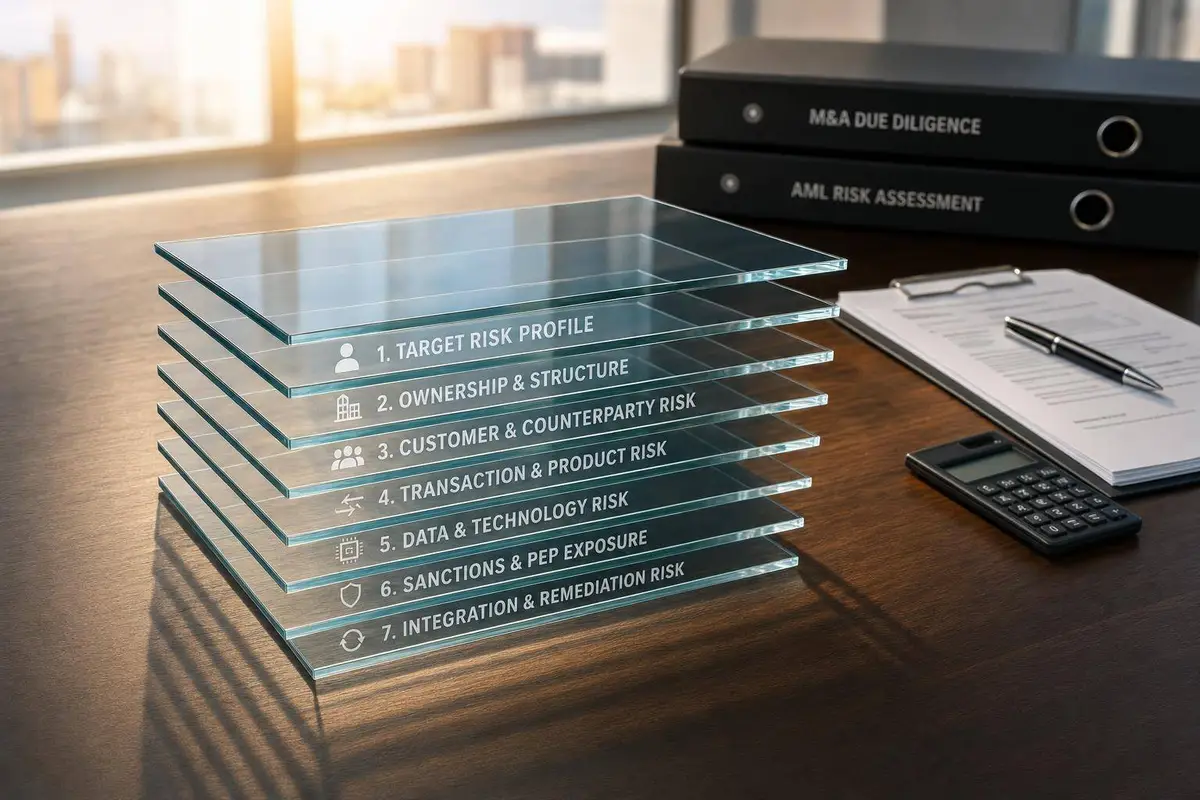
Here are the 7 main AML risks the article covers:
- Weak or missing AML program
- Incomplete KYC and ownership records
- High-risk customers or geographies
- Monitoring gaps and weak SAR handling
- Sanctions, PEP, and adverse media failures
- Governance and compliance culture gaps
- Poor data quality and weak integration readiness
A few points matter most right away:
- KYC and sanctions issues can stop a deal before closing
- Manual systems and weak records can slow financing options
- Post-close AML alignment often takes 12 to 18 months
- High-risk policy alignment should start in the first 90 to 180 days
- Older files, especially pre-2018, often need close review

Key Risks in Anti-Money Laundering (AML) and How to Mitigate Them
Quick Comparison
| Risk | What can go wrong | What I’d check first | Deal effect |
|---|---|---|---|
| AML program | Missing rules, weak testing | Exam reports, AML tests, sample files | Price cuts, cleanup work |
| KYC/ownership | Missing customer or owner data | High-risk files, UBO support | Lender delays, deal risk |
| Customer/geography | Risky clients or places | Account samples, payment flows | Repricing or carve-outs |
| Monitoring/SARs | Missed suspicious activity | Alerts, logs, SAR history | Post-close control gaps |
| Sanctions/PEPs | Blocked parties or hidden ties | Screening logs, ownership checks | Deal pause or stop |
| Governance | Poor oversight, weak escalation | Audit items, staff interviews | Harder remediation |
| Data/integration | Incomplete files, bad records | Random file testing, system fit | Slower closing and integration |
Bottom line: if ownership is unclear, screening is weak, or monitoring cannot be shown with records, I would treat AML as a core deal issue—not a back-office task—and leverage expert advisory services to navigate these risks.
Why AML Due Diligence Matters in SMB and Mid-Market Deals
In SMB and mid-market deals, AML risk often hides in plain sight. It shows up in missing evidence: stale policies, incomplete KYC files, thin ownership records, and manual controls. That may sound like back-office clutter, but it can hit the deal where it hurts most: valuation, financing, and closing speed.
After closing, the buyer takes on the target’s unresolved AML risk. So this review isn’t just about checking whether compliance files exist. It comes down to a simple point: can the buyer verify the target fast enough for lenders, legal counsel, and the closing process?
This is where centralized data rooms and AI-assisted review can help. They can move KYC checks, transaction-log analysis, and issue tracking along with less back-and-forth.
How AML Issues Affect Valuation, Financing, and Closing Timelines
When AML problems come up during diligence, the money impact can be immediate. Known risks can trigger purchase price deductions, escrow holdbacks, or Material Adverse Change clauses tied to enforcement actions. In tougher situations, banks may refuse to process payment flows if ownership, source of funds, or control can’t be verified.
Timelines can slip too. Buyers may demand fixes before closing, or regulators may ask for more information. Full compliance integration after close usually takes 12 to 18 months, and high-risk areas like BSA/AML should be aligned within the first 90 to 180 days.
What Is Often Missing in Smaller Target Companies
Smaller target companies often have the same problem: the paper trail is too thin. Buyers should pay close attention to the gaps below.
| Missing Element | Impact on the Deal |
|---|---|
| Stale KYC files | Delays lender underwriting and bank onboarding |
| Opaque beneficial ownership | Can lead to immediate deal termination if sanctions are found |
| Manual monitoring systems | Increases post-close remediation costs and regulatory friction |
| Weak audit trails | Prevents legal counsel from certifying the deal structure with confidence |
There are other weak spots that show up again and again. Watch for unclear steps for escalating suspicious activity, weak alert investigation methods, uneven staff training, and no independent AML audits or testing.
“Identity must be verified. Beneficial ownership must be transparent. Source of funds must be traceable. Sanctions, PEP, and jurisdictional exposure must be cleared.” — Etienne van den Peereboom, Author
The seven risks below show where AML diligence most often breaks down.
1. Undocumented or Weak AML Compliance Program
A missing AML program is a major red flag in SMB and mid-market deals. And when the AML program is weak, the problem usually goes well beyond AML itself. It often points to bigger gaps in KYC, transaction monitoring, and governance.
If the target has old policies or no independent AML testing, the buyer takes on that risk the moment the deal closes. A major acquisition can transfer a target’s AML failures directly to the buyer, creating post-close enforcement and remediation risk.
During diligence, ask for the last three examination reports, the last two independent BSA/AML tests, and sample high-risk customer files. Those materials help you check whether onboarding, ownership, and escalation controls are complete.
If the program looks weak, work on the assumption that remediation starts at close, not after integration. After closing, map the acquired accounts right away and tackle the highest-risk gaps first.
2. Incomplete KYC and Beneficial Ownership Records
KYC gaps can turn into one of the most costly issues a buyer takes on in M&A. If the target doesn’t have complete KYC files or clear beneficial ownership records, that risk can pass to the acquirer at closing. And that can hit lender approval and deal certainty. That’s why KYC and ownership files should be checked early.
During diligence, the clearest red flags are hidden ownership structures. Think shell entities, layered holding companies, or nominee setups with no clear business reason. Another warning sign is any hesitation from the target or its owners when asked to disclose ultimate beneficial owners (UBOs). It also makes sense to look closely at accounts opened before the 2018 CDD rule, since beneficial ownership records from that period are often incomplete or missing.
The practical step here is simple: verify the files yourself. Don’t lean on target summaries. Review high-risk files on your own and test them for onboarding completeness and ownership accuracy.
If the gaps are material, move fast. Treat remediation as a closing condition. The usual path looks like this:
- Identify major policy gaps within 90 days
- Align high-risk BSA/AML and KYC policies within 180 days
- Finish full harmonization within 12 months
AI can help with the heavy lifting. It can audit legacy KYC files for missing or outdated records. And a VDR can centralize ownership disclosures while keeping a defensible audit trail.
3. High-Risk Customer and Geographic Exposure
If a company serves high-risk customers or does business in high-risk jurisdictions, that risk does not stay behind when the deal closes. It moves to the buyer. In diligence, the main issue isn’t whether risk is present. It’s how concentrated it is and how hard it will be to fix.
Wells Fargo’s 2008 acquisition of Wachovia is the clearest example: inherited AML failures turned into a $160 million post-close liability.
During diligence, pay close attention to customer type and geography. Common warning signs include:
- Heavy MSB, correspondent, or shell-entity exposure
- A large share of customers in high-risk jurisdictions
- Poorly documented payment flows
- Structuring meant to avoid reporting thresholds
Those signals need to be checked file by file, not waved through at a summary level, but managed within a secure deal room.
Sample high-risk files yourself. Don’t lean on roll-up reports. Pull a random set of high-risk accounts and test each one for onboarding completeness and beneficial ownership data. If a client segment falls outside your risk appetite, cut it from the deal or reprice for the risk.
After closing, the work needs to shift into operations right away. The buyer’s BSA program should cover all inherited accounts on Day One, and transaction monitoring should be lined up within 90 days. Use manual monitoring while systems are being migrated, and deploy AI to flag unusual activity and speed KYC file reviews during integration.
4. Transaction Monitoring Gaps and SAR Weaknesses
High-risk customers only matter if the target can spot and escalate suspicious activity tied to them. If transaction monitoring is weak, that problem can slide right past diligence and land on the buyer’s desk at closing. At that point, you’re not just inheriting a system issue. You’re inheriting a control failure.
SAR volume should line up with the target’s risk profile. If a business of that size and complexity has filed too few SARs, that’s a red flag. It’s not proof that everything is clean. Late filings, missing escalation records, and thin investigator notes often signal the same thing: the monitoring program may look fine on paper, but in day-to-day use, it isn’t doing the job. In diligence, the fastest reality check is simple — see whether the program caught these patterns in actual case files.
During diligence, test the system directly. Review samples of alerts, investigations, and transaction logs to confirm that unusual activity was flagged, escalated, and documented. Pay close attention to transaction red flags such as:
- Third-party pass-through payments
- Unrelated foreign funding
- Rushed capital movement
If the target uses a different monitoring system, begin interim manual monitoring on Day One. Then line up thresholds, alert logic, and policies within 90 to 180 days. AI can help spot structuring and unusual payment patterns that manual reviews miss.
5. Sanctions Screening, PEP, and Adverse Media Failures
Screening failures are the next AML risk layer after transaction monitoring gaps. And this layer can hit harder.
A sanctions failure doesn’t just mean the target broke an internal rule. It can make the transaction unlawful. If a target’s beneficial owners, directors, or key intermediaries show up on sanctions lists, the deal may need to stop altogether, not merely pause.
PEP exposure is different. It usually doesn’t kill a deal, but it does trigger EDD. That means you need to identify close associates, verify source of wealth, and escalate the case to senior management. In smaller targets, this step often gets skipped. Many rely on self-disclosure instead of systematic checks, and that’s exactly how PEP exposure slips through.
The fallout can be immediate and expensive. In 2023, a European fintech firm acquired a crypto exchange and was fined €35 million just six months after closing. The fine came because the target had failed to screen transactions involving digital wallets tied to sanctioned jurisdictions before the acquisition. Once the deal closed, that liability moved to the buyer.
Adverse media is the quietest risk in the group. It doesn’t always show up in transaction data or ownership charts. But negative news linking a target or its owners to fraud, corruption, or financial crime can spill over to the buyer’s reputation, even when the events happened years before closing.
Here’s where the weak spots tend to show up:
| Screening Area | Common SMB/Mid-Market Gap | Post-Closing Standard |
|---|---|---|
| Sanctions | Ad hoc or manual checks; missing SDN/LEI reviews | Real-time global screening with automated logs |
| PEP Identification | Reliance on self-disclosure; no EDD applied | Automated PEP verification and link analysis |
| Adverse Media | No formal review; reputational risk ignored | Continuous monitoring of global news and legal databases |
| Beneficial Ownership | UBOs not screened against sanctions and PEP lists | Trace ownership to the natural persons who control the target |
These gaps shouldn’t sit in a diligence memo as box-checking notes. They need to be scored based on deal impact.
When issues surface before close, the buyer should act. That may mean requiring remediation, repricing the deal, or carving out the high-risk business before signing.
Ready to Make Your Next Move?
Whether you're buying, selling, or investing — Clearly Acquired gives you the tools, data, and support to close with confidence.
6. Compliance Culture and Governance Gaps
When screening and monitoring break down, the problem usually sits higher up the chain: weak governance. In most cases, these failures don’t come from one-off process mistakes. They trace back to poor oversight, and the buyer takes on that AML exposure and track record at close. Once the deal is done, inherited AML failures can turn into the buyer’s legal and financial problem.
You can often spot these issues in the diligence file. Common warning signs include unresolved audit findings, local-only policies, no clear escalation path, and staff concerns that went nowhere. A target that resists sharing beneficial ownership details during diligence should also put you on alert.
| Governance Red Flag | Diligence Indicator | Risk Implication |
|---|---|---|
| Weak Oversight | Unresolved audit findings or regulatory investigations | Management indifference to compliance failures |
| Weak Accountability | Outdated or localized-only policies | Lack of centralized control and group-wide standards |
| Ineffective Training | No records of regular staff training or updates | Employees unable to identify or escalate suspicious activity |
| Opaque Ownership | Reluctance to disclose UBOs or complex shell structures | Hidden criminal or sanctioned participants |
| Systemic Gaps | Lack of transaction monitoring logs or audit trails | Inability to defend past actions to regulators post-close |
Don’t stop at documents. Speak directly with compliance staff or consultation services and ask what they flagged, who they told, and what happened next. That kind of conversation can tell you more than a policy binder ever will. High turnover on the compliance team, ignored whistleblower incidents, or a group that talks about compliance like it’s an afterthought are all serious signals. It also helps to review past AML activity for repeat gaps instead of isolated misses.
After close, bring policies into line, retrain staff, and make sure reporting lines to the board are clear. That matters most during integration, because inherited AML risk often flares back up at that stage, especially when the target used to operate on its own without central oversight.
7. Poor Data Quality, Documentation, and Integration Readiness
The last AML risk often comes down to operations: are the target’s records clean enough to integrate without slowing the deal? If AML data is weak or inconsistent, a program that looks fine on paper can turn into a closing problem. Gaps like these increase regulatory risk, drag on valuation and integration, and make it harder to confirm what the target actually did. If records can’t be checked fast, the program may be more paper than practice.
During diligence, pull random customer files and check for complete onboarding, beneficial ownership data, and ongoing monitoring records. Give extra attention to legacy files opened before 2018, since those are often missing key items. It also helps to review the target’s last three regulatory examination reports for any Matters Requiring Attention or repeat findings. Those can point to control problems that run deeper than a single file issue.
On Day One, map inherited accounts, patch high-risk policy gaps fast, and keep BSA records intact through integration. AI-enabled tools can automate audits of legacy KYC files and flag missing beneficial ownership data. A centralized virtual data room (VDR) can also keep legacy documents organized, support secure sharing, and maintain a full audit trail. That can cut remediation cost and give the deal team more certainty around close. Utilizing specialized buyer tools can further streamline this due diligence process.
These issues are easiest to compare by severity, which is why the next table scores each risk side by side.
AML Risk Snapshot Table
Use this snapshot to sort urgent deal risks from cleanup work and decide what needs to happen right after close. The point is simple: find the AML gaps that change price, slow funding, or stop the deal from closing.
| Risk Area | Key Red Flags | Primary Diligence Actions | Post-Close Priorities |
|---|---|---|---|
| AML Program & Policies | Missing or outdated written policies; no formal BSA/AML framework | Independent policy review; interview compliance staff | Identify material policy differences within 90 days; adopt unified high-risk BSA/AML and sanctions policies within 180 days; retrain staff |
| KYC & Beneficial Ownership | Missing or outdated KYC records; shell entities; opaque ownership chains; reluctance to disclose UBOs | Sample high-risk customer files; trace ownership through trusts and foundations | Remediate legacy CDD gaps; align onboarding standards with buyer’s program |
| Transaction Monitoring | Manual logs; no automated monitoring; transactions structured to avoid reporting thresholds; unexplained urgency in capital movement | Audit transaction trails; test alert effectiveness; review SAR filing history | Consolidate monitoring systems; automate detection; implement interim controls if systems differ |
| Sanctions & PEPs | Ad hoc screening; missed sanctions/PEP matches; weak adverse-media checks | Check real-time screening logs; audit PEP coverage; test screening infrastructure | Integrate real-time global screening; update risk assessments for the expanded footprint |
| Regulatory History | Open MRAs; repeat exam findings; history of investigations; declining regulatory ratings | Review the last three regulatory exam reports; check for unresolved violations | Build a documented remediation plan with timelines; route unresolved issues into the parent company’s remediation log |
| Compliance Culture & Governance | No board-level AML reporting; high staff turnover in compliance roles; poor recordkeeping | Evaluate board reporting structure; test internal audit coverage | Implement group-wide ethics and training framework; align reporting, training, and governance cultures |
| Data Quality & Integration | Inconsistent customer records; legacy files missing beneficial ownership data; manual workarounds | Pull random legacy files; assess data migration readiness; check system compatibility | Consolidate systems within 12–18 months; verify BSA records are preserved for five years |
Two issues sit at the top of the pile: sanctions screening and KYC failures. They need the fastest response because the buyer has to verify ownership and clear sanctions exposure before closing. If those pieces are shaky, the deal can stall fast.
By contrast, data and system integration gaps tend to matter most in the first 6 to 18 months after close. They may not always block signing, but they can create major work once the buyer takes control.
Use these scores to shape pricing, reps, escrows, and closing conditions in the framework below.
Applying a Risk-Based AML Framework to M&A
Once you’ve identified the seven risks, the next step is to score each one based on likelihood and deal impact. Use the snapshot table as your starting input, then use those scores to shape price, structure, and closing conditions.
Core Factors to Score During AML Diligence
Each target should be scored across six dimensions. Customer risk is often the first place to look. What share of the customer base includes PEPs, MSBs, casinos, crypto exchanges, or other high-risk entities? And just as important: how clear are the beneficial ownership structures?
Geographic exposure is the next big factor. A target operating only in low-risk U.S. markets will score very differently from one with revenue tied to high-risk or sanctioned jurisdictions. Products and services also matter. Digital payments, offshore wealth management, real estate, and other cash-heavy business models come with higher exposure.
Then look at delivery channels, payment flows, and transaction behavior. Non-face-to-face onboarding, heavy use of intermediaries, or patterns that point to structuring around reporting thresholds will all push the score higher. Last, control strength shows how much cleanup may fall to the buyer after close. That includes governance, KYC records, monitoring logs, SAR history, exam findings, and training.
How AML Scores Affect Deal Terms
Each score should lead to a clear deal response. The table below shows the most common match between risk level and deal-term treatment:
| AML Risk Level | Typical Deal-Term Response |
|---|---|
| Low | Standard reps and warranties; no special AML carve-outs required |
| Medium | Specific AML indemnities; escrow holdback for unresolved red flags |
| High (measurable) | Fixed purchase price deduction; remediation plan attached as a purchase agreement schedule |
| High (unresolvable pre-close) | Condition precedent tied to remediation completion; possible carve-out of a high-risk client pool |
| Critical: sanctions or ownership gaps | Deal paused or terminated until ownership is verified and sanctions exposure is resolved |
When gaps remain, tie remediation timelines directly to the purchase agreement and make closing conditional on completion. Those scores then shape the legal protections that come next.
Legal and Deal-Structuring Protections for AML Exposure
Once the risk score is set, tie each AML issue to a legal fix.
Contract Terms That Address Known AML Issues
The right protection depends on the type of risk. Use reps and warranties for broad AML risk. Use seller indemnities for known problems, like an open regulatory inquiry or a documented KYC gap.
If the issue can be fixed before closing, use a condition precedent. In plain English: the deal does not close until the seller finishes the agreed remediation. It also helps to place remediation milestones in a purchase-agreement schedule so everyone is working from the same checklist.
Some risks are easier to price than to fix. In that case, a purchase price deduction gives the buyer a fixed offset upfront. If the exposure is uncertain, such as a pending enforcement action, an escrow holdback can set aside part of the purchase price until the matter is resolved.
And this isn’t only about the buyer and seller. Lenders and insurers may also ask for legal protections.
When Lenders and Insurers May Require Added Protections
Lenders may block financing or add AML covenants when source-of-funds issues or compliance control gaps are still unresolved.
Freshfields notes:
“In Warranty and Indemnity (W&I) deals where warranties are covered by an insurer instead of the seller, the buyer typically faces exclusions for AML risks in the insurance policy.”
So buyers shouldn’t assume warranty and indemnity insurance will take care of AML exposure. In many deals, they still need backup warranties from the seller outside the insurance setup. And if possible fines could be material, buyers may also ask for collateral to support the indemnity so the seller can still pay after closing.
These protections should also line up with any AI-assisted diligence and tracking used to manage remediation after signing.
How AI and Modern Deal Infrastructure Can Strengthen AML Review
Once AML risk is identified, the next step is getting the review and cleanup process under control. After risk scoring and deal protections are in place, AI and connected workflows can move AML review along, assign follow-up work, and keep a clear audit trail. Human review still closes the loop.
AI can scan legacy files for exceptions and flag unusual customer activity for review. It can also use pattern analysis to detect anomalies that manual review might miss.
AI can also help sort documents, compare buyer and target AML controls, and rank fixes based on diligence findings. For high-risk files, manual spot checks should stay in place.
Connected deal workflows keep diligence files, remediation tasks, and approvals in one audit trail. That means issues stay tied to owners, deadlines, and closing conditions instead of getting lost across email threads and shared folders.
Clearly Acquired centralizes diligence files, data rooms, and underwriting inputs in one auditable workflow — functioning as one compliance workflow that maps regulatory obligations to unified tasks across legacy and acquired operations.
Conclusion
All seven risks point to the same takeaway: AML diligence needs to be handled before closing, not after it.
Here’s the core issue. Weak AML controls don’t stay with the seller. They pass to the buyer at close. Missing KYC files, unclear ownership, weak monitoring, and poor governance aren’t minor admin problems. They’re process failures that move straight into the deal.
The Wells Fargo–Wachovia case shows how big that exposure can get. Wells Fargo paid a $160 million settlement after taking on Wachovia’s AML failures.
That’s why AML should be treated as a core workstream from LOI through integration. Run sanctions and PEP screening early. Review high-risk files. Use escrow or remediation covenants when gaps show up. And line up policies before close. Clearly Acquired can help keep diligence files, remediation tasks, and deal conditions organized.
In M&A, one of the best ways to cut AML risk is simple: verify early, price it clearly, and document the fix before close.
FAQs
How do I score AML risk in an acquisition target?
Use a risk-based due diligence review to assess the target’s AML program. Review its risk assessment, SAR history, transaction monitoring, and any unresolved audit findings or regulatory warnings from the past one to five years.
Also sample high-risk customer files. Check KYC records and beneficial ownership data, and look for red flags such as opaque ownership, high-risk jurisdictions, or cash-based operations.
If issues show up, deal with them through warranties, escrow holdbacks, or pre-acquisition remediation.
Which AML issues can delay or stop closing?
AML issues can slow a deal down or stop it cold if the target doesn’t meet regulatory standards.
A transaction may be blocked by sanctions exposure, ownership structures that are so opaque the ultimate beneficial owners can’t be verified, or a source of funds that doesn’t line up with the target’s profile.
There’s another problem buyers can’t brush aside: active supervisory investigations or unresolved regulatory audit findings. Those issues can bring a transaction to a halt because the buyer may inherit immediate legal and financial liability at closing.
What AML fixes should happen first after close?
Right after closing, the acquiring firm takes on full legal and financial responsibility for the target’s compliance status. That means the first move should be an immediate internal AML health check to spot gaps, weak points, and mismatches between the acquired company’s setup and your current framework.
At the same time, bring key AML processes into line across both businesses. Align transaction monitoring systems, centralize customer screening, retrain staff on your AML framework, and update reporting duties for any new jurisdictions.
This work needs to happen fast. If the two companies keep running under different AML rules and tools, problems can slip through the cracks. A quick review helps you see where controls are uneven, where data may not match, and where staff may need direction before day-to-day risk starts to build.
About the author
Principal & CEO/CIO
Samson Jagoras has 15+ years across finance, real estate, and business acquisitions. He began his career as a Futures & Commodities broker and later served as Chief Strategy Officer of an INC 500 marketing and technology firm, helping scale revenue from $1M to over $100M. Today he buys, builds, and advises a portfolio of companies with a focus on M&A, capital allocation, and operational strategy.